 SEO & Accessibility
 AI
 Localization
 Ecommerce
 Forms
 Fields
 Development
 Security
 Templating
 Performance
 Control Panel
 Widgets
 Assets
 Utilities
 Mailer Adapters
 Social Networking
 Integrations
Fail2Ban for Craft CMS
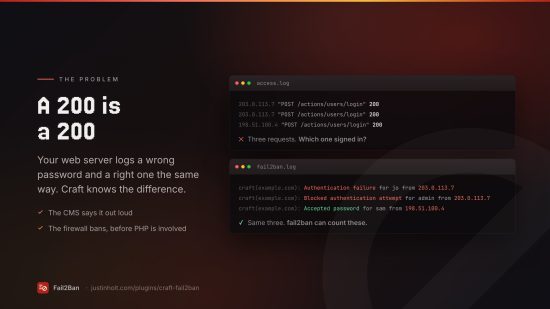
Your web server log shows a 200 for a wrong password and a 200 for a right one. fail2ban is
very good at banning addresses and has no way to tell those apart. Craft knows the difference.
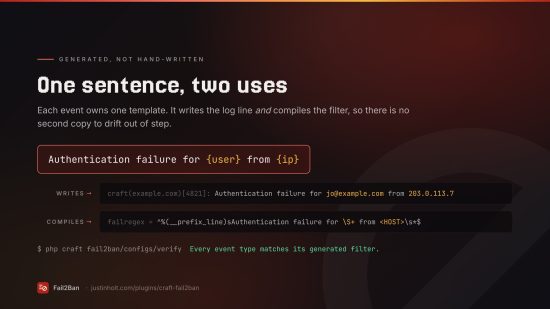
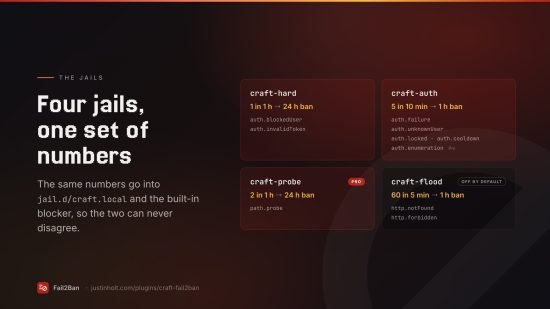
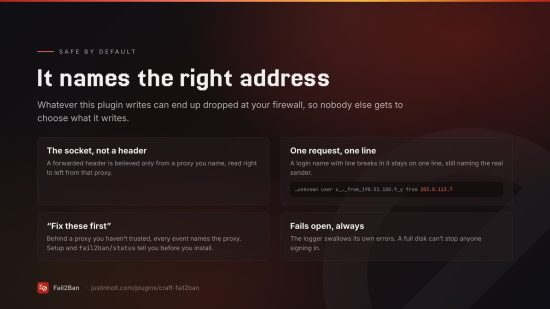
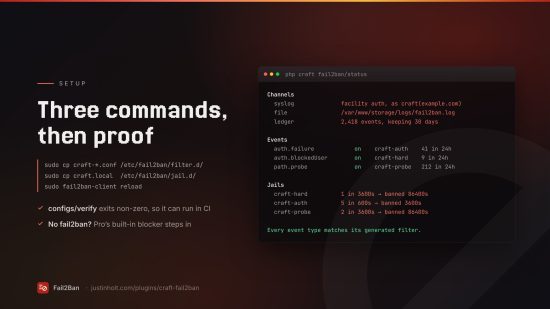
This plugin says it out loud — in the format fail2ban already understands — and lets the firewall do the banning, at the edge, before PHP is involved at all.
2026-08-18T09:14:02+0000 craft(example.com)[4821]: Authentication failure for jo@example.com from 203.0.113.7
2026-08-18T09:14:04+0000 craft(example.com)[4823]: Authentication attempt for unknown user root from 203.0.113.7
2026-08-18T09:14:06+0000 craft(example.com)[4826]: Blocked authentication attempt for admin from 203.0.113.7
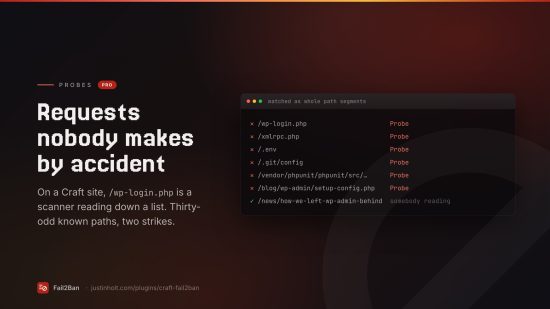
2026-08-18T09:14:09+0000 craft(example.com)[4831]: Probe for /wp-login.php from 203.0.113.7
It is the Craft equivalent of wp-fail2ban, including
the log-line convention — craft(host)[pid]: is the shape fail2ban's own common.conf already
parses, and it is deliberately the same shape wp(host)[pid]: has, so an admin who runs both
knows what these lines are before reading a word of documentation.
Requirements
Craft CMS 5.3+ and PHP 8.2+. No runtime dependencies, no build step, no outbound requests.
fail2ban itself is optional. See Without fail2ban.
Lite
Pro
Plus $29/year after one year.
To install this plugin, copy the command above to your terminal.
This plugin doesn't have any reviews.