 SEO & Accessibility
 AI
 Localization
 Ecommerce
 Forms
 Fields
 Development
 Security
 Templating
 Performance
 Control Panel
 Widgets
 Assets
 Utilities
 Mailer Adapters
 Social Networking
 Integrations

| Feature | Lite (Free) | Pro |
|---|---|---|
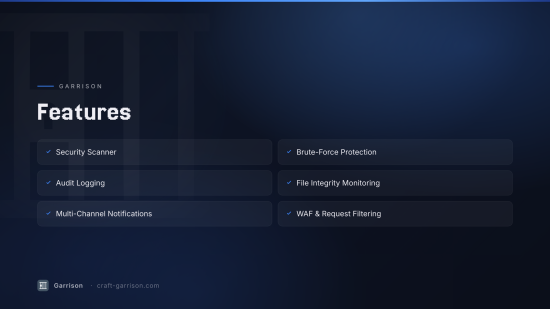
| Security scanner (14 checks) | ✓ | ✓ |
| CMS config / headers / CSP checks | ✓ | ✓ |
| Login brute-force protection | ✓ | ✓ |
| Audit logging | 30 days | 365 days |
| Console commands | ✓ | ✓ |
| Scan history | Last 10 | Unlimited |
| Scheduled scans (queue-based) | — | ✓ |
| CP alerts on failed scan | — | ✓ |
| Email notifications | — | ✓ |
| Slack / Discord / Webhook | — | ✓ |
| IP restriction (CP + frontend, CIDR) | — | ✓ |
| HTTP Basic Auth | — | ✓ |
| File integrity monitoring | — | ✓ |
| REST API | — | ✓ |
| Multi-site scans | — | ✓ |
| Rate limiting | — | ✓ |
| WAF / request filtering | — | ✓ |
| Geo-blocking | — | ✓ |
| Dashboard analytics + trends | — | ✓ |
| Risk score trending | — | ✓ |
| Auto-remediation suggestions | — | ✓ |
Modules
Scanner
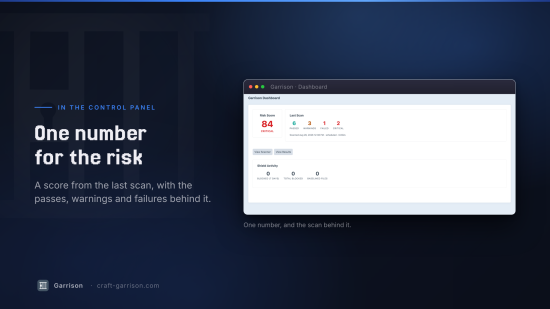
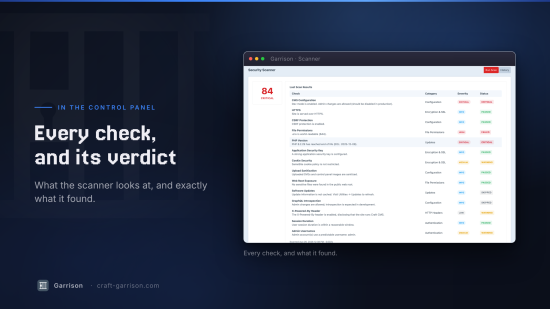
Runs 14 security checks against your site and produces a risk score (0–100):
- CMS Configuration — dev mode, admin changes, test email, session duration, GraphQL origins
- HTTPS — verifies site is served over TLS
- CSRF Protection — confirms CSRF tokens are enabled
- File Permissions — checks .env, config/, web/index.php for unsafe permissions
- PHP Version — flags EOL or soon-to-expire PHP versions
- HTTP Headers — X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy
- Content Security Policy — checks for CSP header presence and configuration
- CORS — validates cross-origin resource sharing settings
- CMS Version — flags outdated Craft CMS installations
- Plugin Versions — checks for plugins with available updates
- Database Security — table prefix usage, default credentials
- Admin Accounts — flags accounts using weak or default usernames
- SSL Certificate — checks certificate expiry
- File Permissions (detailed) — world-readable/writable sensitive paths
Risk score weights: Critical (+25), High (+15), Medium (+8), Low (+3), Warning (+1).
Shield
Active request-level protection. Checks run on every request, ordered cheapest to most expensive:
- IP blocklist — in-memory cached lookup → 403
- Login lockout — brute-force threshold check → 403
- IP allowlist — optional restrict-to-list mode → 403
- Geo-blocking (Pro) — country-based blocking → 403
- Rate limiting — cache-based atomic increments → 429
- WAF rules (Pro) — compiled regex patterns for SQL injection, XSS, path traversal, user-agent filtering → 403
Sentinel
Monitoring and audit trail:
- Audit log — tracks logins, logouts, failed logins, element saves/deletes, plugin installs, project config changes, user events
- File integrity (Plus+) — SHA-256 baselines stored in the database; detects modified, added, or deleted files in monitored paths
Default monitored paths: vendor/craftcms/cms/src/, config/, .env, web/index.php.
Beacon
Multi-channel notifications (Pro+):
- Email — via Craft's built-in mailer
- Slack — webhook URL
- Discord — webhook URL
- Webhook — generic POST with JSON payload
Triggers: scan failure, threat detection, login lockout.
Lite
Pro
Plus $79/year after one year.
Installation Instructions
To install this plugin, copy the command above to your terminal.
Reviews
This plugin doesn't have any reviews.
Active Installs
9
License
Craft
Last release
October 5, 2026
Activity (30 days)
1
Closed Issues
0
Open Issues
0
Merged PRs
0
Open PRs